The SSH Agent on Linux holds your SSH keys (and certificates) in memory ready to be used by SSH when connecting to a server.
Assuming you already have a key pair, loading the SSH Agent and adding a key is as simple as doing the following. Note I’m assuming for this example your Private Key is in the file: ~/.ssh/id_ed25519, if you have a passphrase on this (which you should), you’ll be prompted to enter it.
$(ssh-agent -s)
ssh-add ~/.ssh/id_ed25519
Now the key is loaded, you should be able to see it with:
ssh-add -lAnd your key should then be listed, for example:
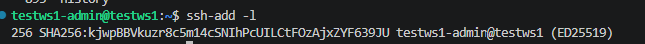
Now assuming you have your public key on a remote server, you can just SSH to it as follows, in my example I’m logging on as the ansible user on the remote machine that has my Public Key deployed.
ssh ansible@192.168.102.201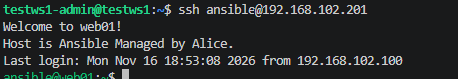
Of course, if you wanted to login and specify the key file directly, i.e. not using the SSH Agent, you can with the following:
ssh -i ~/.ssh/id_ed25519 ansible@192.168.102.201Make it Automatic
So, to make this a bit more straight forward, we can make the SSH Agent load at the point when you login to your management machine. We first edit your BASH profile.
vi ~/.profileThen add the following to the bottom of the file.
# Load SSH Agent
if [ -z "$SSH_AUTH_SOCK" ] ; then
    eval $(ssh-agent -s)
    ssh-add
fi
You’ll notice the ssh-add line, this just loads all or any keys into the SSH agent that are in the default .ssh key location, i.e. ~/.ssh/, if you want to specify a specific key, then you need to change the ssh-add line to include the path to the private key of your choice.
If however you just want it to start the SSH Agent automatically, just leave this line out.
Passphrases
A note about passphrases. You should have a passphrase added to your SSH Keys as a matter of course, because of this you’d need to enter the passphrase on each logon so the SSH Agent can access and load the key. This can become tiresome, so its recommended to just load in the key you need when you need it, just use the SSH Agent automatically being loaded instead.