Get List of Listening Ports (Linux)
To see a list of listening ports on a host you can run: You can also filter with the below, in this example filtering to port 22 (SSH):
The ramblings of a computer geek
To see a list of listening ports on a host you can run: You can also filter with the below, in this example filtering to port 22 (SSH):
Netcat (nc) is a simple, but very useful tool to perform connection tests and scans on your network. Its helpful to quickly check if a port is open (and listening) on a remote machine and that firewall change you made is working as expected. Here i’ll provide some simple examples for you to try. Check … Read more
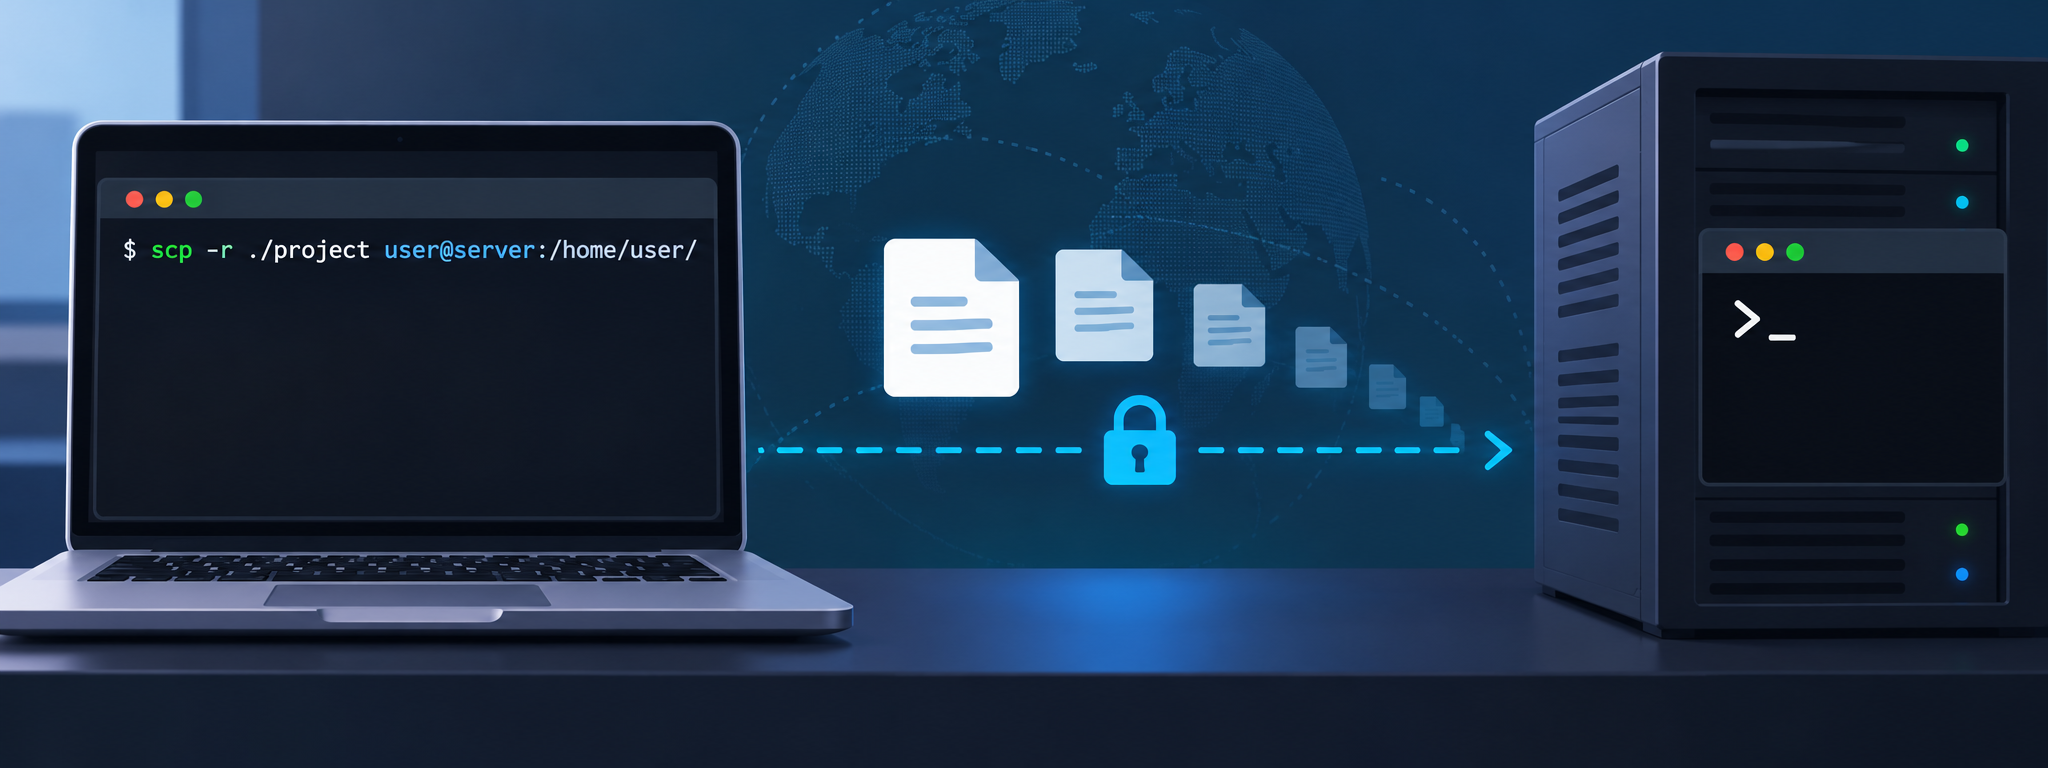
SCP (Secure Copy Protocol) is a useful command to copy files between systems, we’ll explore a few example scenarios that you’ll commonly use. I’m not going into great detail about all the various arguments and options you can use, these you can find in other articles elsewhere. Instead this is going to be a very … Read more

GNS3 can run on Windows, Linux or MacOS, however for large scale network simulations running it on a dedicated server machine (typically Linux) is recommended. The deployment of this can be difficult due to limited documentation, the following provides a guide for the installation of GNS3 on a dedicated Linux server, ideally with as much … Read more
Although not good security practice, it can be helpful for a user to account to have at least some (or all) sudo ability without the need to re-enter the user’s password to gain sudoers. By adding the user within the file /etc/sudoers (via visudo is recommended for Ubuntu Linux), with the following, you can ensure … Read more
In part 4 of the series we are exploring Metrics. Although we’ll go into more detail later on in the series. Kubernetes can collect metrics of attributes like CPU or Memory etc. These metrics are collected by a Metrics Server, you can use the built in Kubernetes one (Metrics Server), or you can use external … Read more
We had an interesting issue where our EXIM configuration was flattening a subdomain’s “From” address, i.e. it was re-writing an email’s From (HFrom) and MailFrom (return-path/envelope-from) headers to @domain.com addresses, i.e. to catch emails such as root@mymachine.domain.comand re-write the From (HFrom) and MailFrom (return-path/envelope-from) to root@domain.com instead. Problem was, this configuration wasn’t documented, so needed a bit of investigation; but is also a good learning point … Read more
Firstly, a disclaimer. Although you can store values, specifically secrets (e.g. passwords) within Environment Variables so that you are not storing them in your Terraform template code there are better ways, for example by use of a formal Secrets Management solution. However, this article will show you how you can use Environment Variables to “safely” … Read more

Following on from a previous article https://geekmungus.co.uk/?p=4510 we now investigate some more into using Ansible for configuration management and installations. As something we can use as an example, we’re going to setup a simple Bind DNS server, which we can use to explore how to manage the installation of Bind and it’s configuration within Ansible. … Read more
Although there are other ways to do it, here is a quick way to tree list directories and files: